Technology leadership for startups

You built the product.
Let’s build what comes next.

From your first MVP to your next stage of growth. Get experienced, hands-on technical leadership to make your product secure, reliable, and ready to scale.

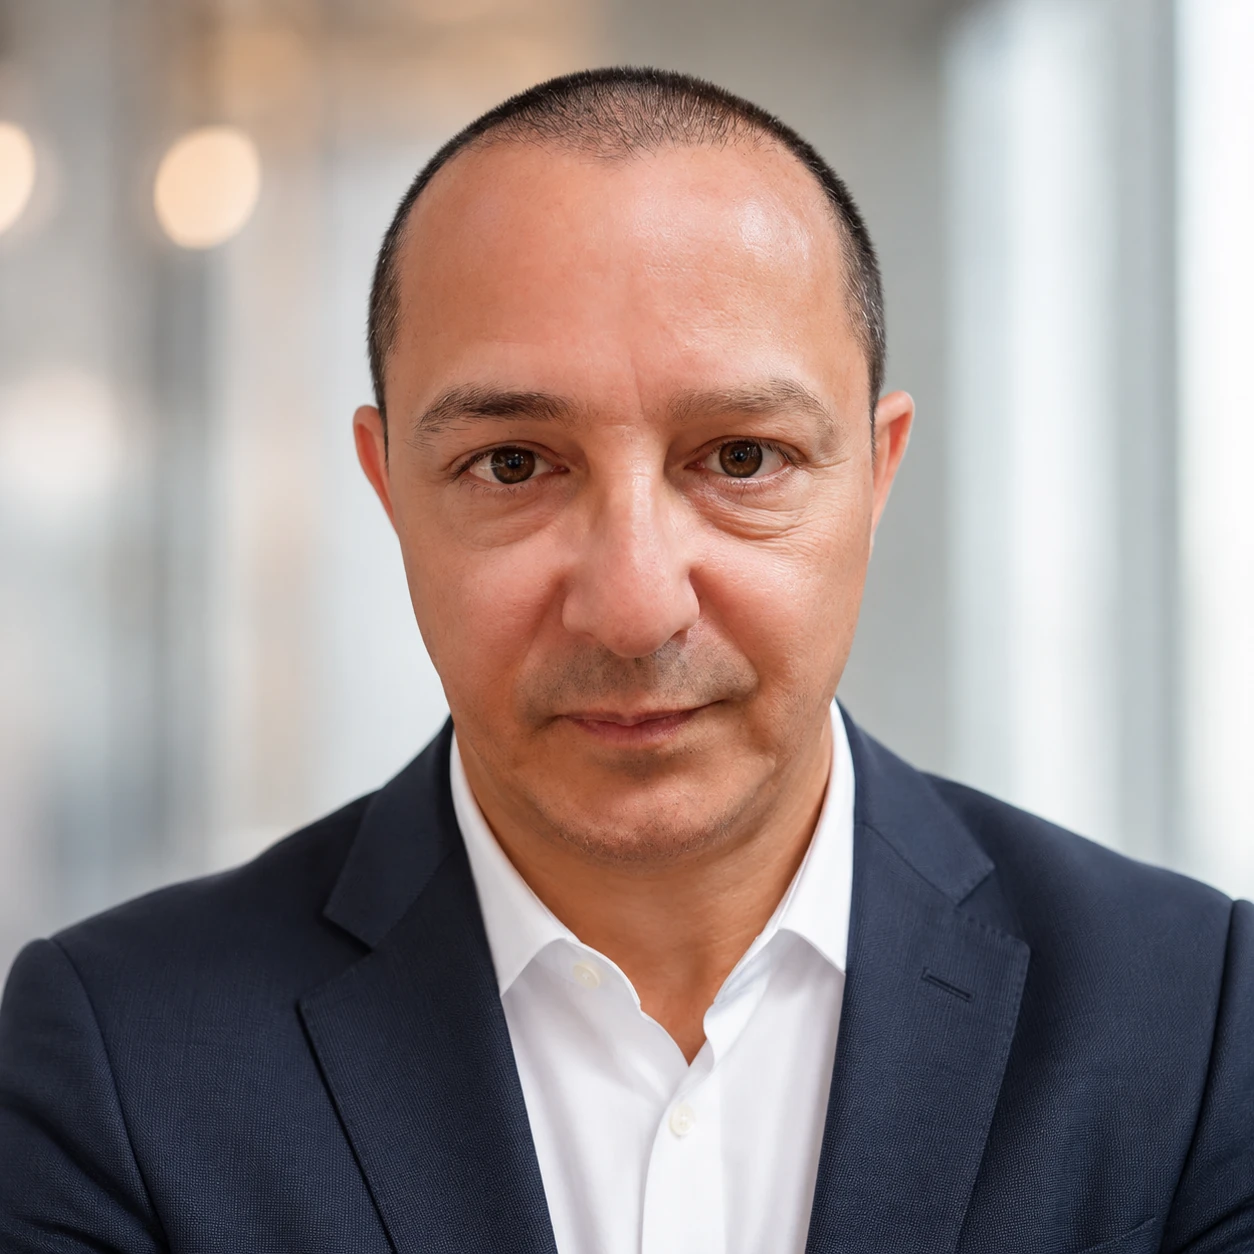
Work directly with Amine Nabi, CTO of BNMA. 30+ years in software.

What you gain

Protect the product you’ve worked so hard to build.

A polished demo can hide exposed credentials, missing access checks, runaway API costs, or recovery plans that have never been tested. We help you find the gaps before they become business problems.

01

Protect your customers and their trust.

Make sure the right people can access the right data, and keep privileged controls out of the client.

How we help

Review authentication, backend permissions, secret handling, and customer data boundaries. Identify what needs fixing and why.

02

Keep usage from becoming a surprise bill.

Your growth should not depend on hoping nobody abuses an expensive endpoint.

How we help

Define rate limits, usage budgets, processing limits, and alerts around AI, SMS, uploads, exports, and other costly operations.

03

Keep shipping with a recovery plan.

Know how to spot a failure, restore your data, and recover from a release that goes wrong.

How we help

Strengthen deployments, monitoring, backups, restore procedures, and day-to-day technical ownership.

04

Be ready for harder customer questions.

Understand your data, vendors, and obligations before an enterprise security review or healthcare opportunity exposes a gap.

How we help

Prepare technical evidence, review privacy and compliance readiness, and work with specialists on requirements such as HIPAA where applicable.

Start with the questions your demo cannot answer.

Check your app’s readiness

The app readiness check

Your app works.
What did you miss?

Walk through 16 questions founders can easily overlook. Each one connects a technical detail to a possible business problem and the work needed to address it.

Choose what you can verify today. “Not yet” and “Not sure” build your review list. Answers stay on this page and clear when you reload.

01 / Accounts & access

A login screen is only the beginning of protecting an account.

01Are login attempts and password resets protected against repeated abuse?

What could go wrong

Unlimited attempts can let bots keep guessing passwords or flood your users with reset messages. A reset flow can become an easier route into an account than the login screen.

How BNMA helps

Review account and network-based throttling, reset-token expiry, abuse alerts, and recovery flows without making it easy to lock legitimate users out.

02Are privileged API keys and authentication secrets kept out of the browser?

What could go wrong

Secret keys shipped in frontend code or a mobile app can be extracted and reused. Hiding or renaming them does not make them private. Some publishable keys are intentionally public; privileged credentials are different.

How BNMA helps

Identify each key’s permissions, move privileged calls behind the server, rotate exposed secrets, and use controlled secret storage.

03Does the server verify admin permissions on every protected action?

What could go wrong

Hiding the admin menu or checking a role only in the client does not protect the underlying API. Someone could reach privileged operations even when the interface never shows them.

How BNMA helps

Enforce permissions in the backend, deny access by default, and test protected actions independently of the interface.

04Have you tested that one customer cannot access another customer’s records?

What could go wrong

A valid login does not mean a user should see every record. Missing ownership checks can expose another customer’s documents, exports, or account data.

How BNMA helps

Review tenant and record-level access across queries, downloads, background jobs, and APIs. Add tests for users who must be denied access.

02 / APIs & spending

A feature that costs money to run needs limits that hold up outside the interface.

05Do expensive API endpoints have enforced usage and spending controls?

What could go wrong

Repeated AI calls, SMS messages, large exports, or media jobs can consume your budget and capacity. A disabled button in the app does not stop direct requests. A billing alert alone does not stop spending.

How BNMA helps

Set server-side quotas, endpoint rate limits, concurrency limits, payload caps, and timeouts. Add provider spending caps where available and alerts with an owner.

06Does the backend check what a user is allowed to buy, use, or change?

What could go wrong

If the server trusts a price, subscription tier, or permission sent by the browser, a modified request may unlock paid features or change a transaction.

How BNMA helps

Calculate prices and enforce entitlements from trusted server records. Validate every operation before committing changes or starting paid work.

07Are payment callbacks and other webhooks verified and safe to receive twice?

What could go wrong

An unverified callback can be mistaken for a real payment. A legitimate event delivered twice can also trigger duplicate fulfillment, credits, or notifications.

How BNMA helps

Verify provider signatures, reject invalid events, and track processed events so retries do not repeat the business action.

08Are uploads and user input validated on the server, with resource limits?

What could go wrong

Browser validation can be bypassed. Oversized uploads, unexpected input, and unsafe file handling can exhaust resources or expose your app to malicious content.

How BNMA helps

Validate types and sizes on the backend, bound expensive operations, use safe database queries, and isolate or scan uploads where appropriate.

03 / Data & compliance

Know what data you hold, where it travels, and which obligations apply to your business.

09If your app handles health information, have you established whether HIPAA applies?

What could go wrong

HIPAA applies to covered entities and business associates, not automatically to every health app. Where it applies, encryption alone is not a complete compliance program. Missing requirements can affect your design and customer agreements.

How BNMA helps

Map the data and business relationships with qualified legal or compliance specialists. Translate applicable requirements into access controls, auditability, risk assessment, and operating procedures.

HHS: when HIPAA applies

10Have you checked which vendors receive sensitive data and what agreements you need?

What could go wrong

Health information can reach cloud storage, support tools, analytics, or AI providers through an overlooked integration. Where HIPAA applies, relevant cloud providers may require a business associate agreement even when stored data is encrypted.

How BNMA helps

Inventory data flows and vendors, confirm service scope and required agreements with specialists, and prevent sensitive data from entering tools that are not approved for it.

HHS: cloud services and HIPAA

11Do your data collection, retention, and deletion flows match your privacy commitments?

What could go wrong

A delete button may remove the visible account while records remain in exports, connected services, or backups. A privacy policy that does not match actual behavior can create customer and compliance problems.

How BNMA helps

Map the data lifecycle, minimize unnecessary collection, and define deletion and backup-retention behavior against the requirements that apply to your product.

12Are private files, logs, and error reports protected from unintended exposure?

What could go wrong

A protected app can still leak data through public storage, long-lived download links, debug output, or logs containing tokens and personal information.

How BNMA helps

Review storage permissions and download access, redact sensitive values, limit log access, and keep useful audit records without logging credentials.

04 / Launch & recovery

The next test is what happens when a release, dependency, or production service fails.

13Have you restored a backup and checked that the product actually works afterward?

What could go wrong

A successful backup notification is not proof that you can recover. Missing files, unavailable keys, or untested restore steps can turn a database problem into a much longer outage.

How BNMA helps

Test restoration of data and files, verify required credentials, and agree on acceptable recovery time and data loss with a documented owner.

14Will the right person know when a critical customer workflow stops working?

What could go wrong

A running server can still have broken signups, failed payments, stalled jobs, or rising API errors. Customers may discover the failure before your team does.

How BNMA helps

Monitor critical workflows, failures, latency, and spend. Route actionable alerts to a named owner and document how to investigate.

15Can you release, roll back, and recover database changes without improvising?

What could go wrong

A rushed deployment can break production, and a code rollback may not undo a destructive database change. Test environments using live credentials can also affect real customers.

How BNMA helps

Separate environments and credentials, add release checks, plan safe migrations, and rehearse rollback and recovery procedures.

16Are sessions, team access, dependencies, and production credentials actively maintained?

What could go wrong

A former contractor may retain access, an old session may remain valid, or a vulnerable package may stay deployed because nobody owns the follow-up.

How BNMA helps

Review session expiry and revocation, require strong admin authentication, remove stale access, rotate credentials when needed, and assign dependency updates to an owner.

Security and compliance references

The checks reflect established guidance on authentication, authorization, secrets management, and API resource limits from OWASP. HIPAA questions link to HHS guidance in the Data & compliance category. Requirements depend on the product, data, and business relationships.

How we help

From unanswered questions to a working plan.

We review the actual code, infrastructure, and data flows. Then we prioritize the risks, preserve what works, and help you close the gaps through guidance or hands-on implementation.

01 / ASSESS

Assess & stabilize

Understand the platform and identify the most important technical risks.

  • Review architecture, code, and data
  • Assess infrastructure and security
  • Identify technical debt and reliability risks
  • Prioritize critical remediation
02 / PREPARE

Secure & prepare

Strengthen the controls your product needs for real-world use.

  • Authentication and access control
  • Data protection and secrets management
  • Rate limiting and audit logging
  • Backups, recovery, and environment separation
  • Privacy and compliance readiness
03 / OPERATE

Deploy & operate

Make the platform easier and safer to run with clear operational visibility.

  • Production infrastructure and CI/CD
  • Monitoring, logging, and alerts
  • Repeatable deployment processes
  • Backups and recovery procedures
04 / EVOLVE

Complete & evolve

Finish what the next stage needs and create a practical technical roadmap.

  • Priority features, admin tools, and integrations
  • Performance and development process improvements
  • Technical roadmap and hiring plan
  • Customer and due diligence readiness

The level of involvement follows your engagement. In Technical Advisory, I guide and review while your team implements. Technical Lead and Fractional CTO engagements include hands-on execution.

Three ways to work together

The right level of leadership.
For the stage you’re at.

You may have developers, an agency, or a product you built yourself. Choose the level of ownership you need, without hiring a full-time CTO.

01 / Guidance & oversight

Technical Advisor

$4,000/ month

You have people building the product. Get an experienced technical leader reviewing the work and helping you make better decisions.

Discuss technical advisory
  • Weekly technical working session
  • Weekly GitHub and codebase review
  • Architecture and technical decision support
  • Security, privacy, and scalability review
  • Risk prioritization and roadmap input
I guide. Your team implements.I identify issues and recommend solutions. Your team owns implementation, deployment, remediation, and delivery.
Explore the advisory scope

What I review and guide

  • Application architecture and major technical changes
  • Security, privacy, scalability, and maintainability
  • Infrastructure, database, and API design
  • Integration strategy and build-versus-buy decisions
  • Technical debt, risks, and priorities
  • Product roadmap and technical direction

Best for your startup if

  • You already have developers, an agency, or an offshore team
  • You are a non-technical founder who wants an independent perspective
  • You need someone experienced reviewing architecture and code
  • You want to catch problems before they become expensive to reverse
  • You need help making decisions while your team builds the product

03 / Company-level leadership

Fractional CTO

$15,000/ month

You need a technology leader alongside the founder. Someone to own the technology function as well as the codebase.

Discuss a fractional CTO
  • Everything in the Technical Lead engagement
  • Product strategy and technology direction
  • Security, privacy, and compliance readiness
  • Customer, partner, and investor support
  • Engineering hiring and team leadership
I own the technology function.Executive leadership with hands-on architecture and engineering, connecting technical decisions to the company’s future.
Explore the fractional CTO scope

Technology ownership

Architecture, engineering, infrastructure, security, data and integration strategy, development standards, reliability, technical risk, scalability, maintainability, technology selection, and long-term technical evolution.

Product strategy

Work directly with founders and product leadership on product direction, feature priorities, MVP decisions, customer workflows, platform capabilities, feasibility, cost and complexity tradeoffs, roadmap sequencing, and build-versus-buy decisions.

Security, privacy & compliance

Turn requirements into concrete engineering decisions: data protection, authentication, role-based access, encryption, audit logging, secrets management, vendor security, backup and recovery, privacy requirements, security questionnaires, technical policies, and compliance readiness. Coordinate with legal, compliance, security, or regulatory specialists where needed.

Customers, partners & investors

Represent the technology side in enterprise customer conversations, technical sales, partner meetings, vendor negotiations, security reviews, architecture discussions, product demonstrations, investor meetings, technical due diligence, and board-level discussions.

Fundraising & due diligence

Prepare technical pitch materials, architecture summaries, product and technology narratives, roadmaps, and diligence responses. Review technical claims and identify risks before they surface in diligence.

I support the technical side of fundraising. The founder remains responsible for investor outreach.

Engineering team & hiring

Determine when to hire, define roles and hiring profiles, interview candidates, evaluate agencies and contractors, select development resources, onboard engineers, establish standards, mentor the team, and define ownership as the organization grows.

Founder-level technology support

Ongoing support for decisions about scope, feasibility, timelines, architecture, security, vendors, hiring, customer requirements, partnerships, infrastructure, cost, development priorities, and technical risk.

Best for your startup if

You do not have a CTO, technology is central to the business, and you need hands-on execution with executive leadership. You may be preparing for customers, partnerships, fundraising, or an engineering team of your own.
Not sure which level fits? Start with where your product is today.

Compare the responsibilities

A clear division of responsibility

Advice. Execution. Leadership.

Each engagement reflects a different level of ownership. Here is how they compare.

Monthly engagements and the responsibilities included in each.
Your level of supportTechnical Advisor$4,000 / monthTechnical Lead$12,000 / monthFractional CTO$15,000 / month
Technical guidanceIncludedIncludedIncluded
ArchitectureReview & guidanceFull ownershipFull ownership
Code reviewIncludedIncludedIncluded
Hands-on developmentYour teamIncludedIncluded
Production deploymentYour teamIncludedIncluded
Infrastructure ownershipYour teamIncludedIncluded
Security implementationYour teamIncludedIncluded
Technical roadmapGuidanceOwnOwn
Product strategyTechnical inputTechnical inputActive leadership
Founder-level technology supportWeeklyRegularOngoing
Customer / partner technical representationLimitedAs neededIncluded
Investor / due diligence supportLimitedTechnical supportIncluded
Engineering hiring & team designGuidanceAs neededIncluded
Technology organization leadershipNot includedNot includedIncluded

On smaller screens, scroll the table horizontally to compare all three engagements.

Where I can help

Across the codebase.
And beyond it.

The work follows the needs of your product and company. Explore the areas I commonly help startups with.

01Architecture & codebase

Architecture and codebase reviews, technical debt, refactoring, backend, frontend and mobile architecture, database and API design, integrations, scalability, performance, and maintainability.

02Production & infrastructure

Cloud architecture, AWS and cloud services, production and staging environments, CI/CD, deployment, monitoring, logging, alerting, backups, disaster recovery, environment management, infrastructure security, and cost optimization.

03Security

Authentication, authorization, role-based access, data protection, encryption, secrets management, API security, rate limiting, audit logging, access controls, secure development practices, vendor risk, and security review.

04Product & roadmap

Technical roadmaps, feature prioritization, MVP decisions, feasibility, architecture sequencing, build versus buy, integration planning, internal and administrative tools, customer workflows, data and analytics, and AI capabilities where they make sense.

05Engineering & team

Developer, agency, and contractor oversight, code review, development standards, testing strategy, release processes, technical documentation, hiring, technical interviews, team structure, developer onboarding, and engineering leadership.

06Business & technology

Customer technical meetings, enterprise sales support, partner discussions, vendor evaluation, technical due diligence, investor questions, pitch-deck technology content, security questionnaires, product demonstrations, and technical risk assessment.

Amine Nabi, CTO of BNMA
30+years designing, building, and leading software

Your technical partner

Leadership that stays close to the work.

Amine Nabi / CTO, BNMA

I am a technology executive and hands-on software architect and engineer with more than 30 years of experience across healthcare, financial services, construction, manufacturing, logistics, media, SaaS, and enterprise software.

My approach is deliberately hands-on. Depending on the engagement, I may be reviewing architecture, writing code, deploying infrastructure, solving production issues, leading developers, interviewing engineers, or joining a customer or investor conversation.

“Make better technical decisions, reduce unnecessary risk, and build technology that can support the business you are trying to create.”

Let’s start with your product

What does your
next stage look like?

You do not need to know which engagement you need. We can start with where your product is today, what you want to accomplish next, and the team you already have.

Schedule a conversation

Technical Advisor $4,000/mo · Technical Lead $12,000/mo · Fractional CTO $15,000/mo